Software & AI Security
We protect software and AI systems. LLM security, prompt injection, AI agents, RAG, Shadow AI, model and MLOps security, AI red teaming, AI gateways and ISO/IEC 42001 — a 12-part guide series prepared by our expert team.
What Is Software and AI Security? New-Generation Cyber Threats in Modern Applications
What is software and AI security? Explore LLM, AI Agent, Prompt Injection, data leakage, model security and Secure AI SDLC risks for modern applications.
Security Risks of AI-Assisted Software Development: AI Code Assistants and Secure Code
Explore the security risks of AI-assisted software development: AI code assistants, insecure code generation, data leakage, SAST and a Secure Coding guide.
What Is LLM Security? Cyber Attacks on Large Language Models and How to Defend Against Them
What is LLM security? Prompt injection, data leakage, insecure output handling, model abuse and the enterprise security controls for large language models.
Prompt Injection and Jailbreak Attacks: How AI Systems Are Manipulated
What are Prompt Injection and Jailbreak? Explore direct and indirect attacks, RAG and AI Agent risks, realistic examples and LLM security controls.
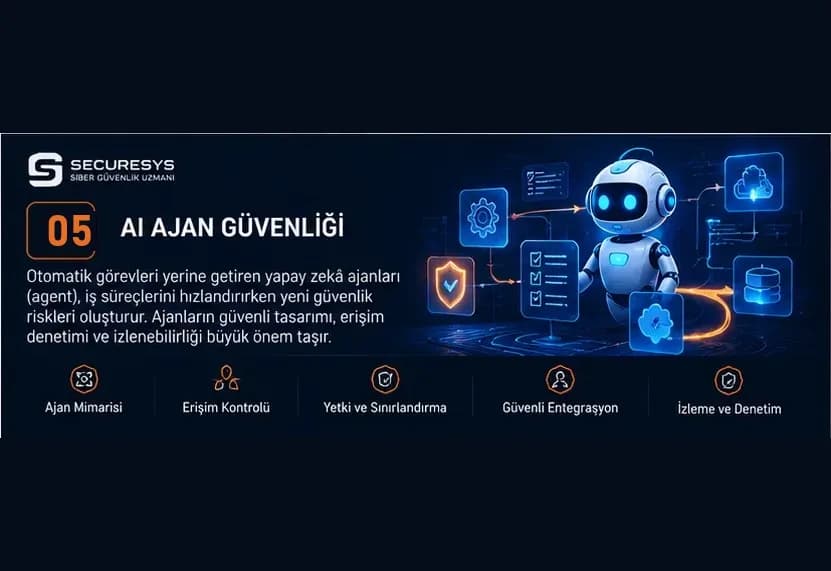
AI Agent Security: Autonomous AI, Tool Calling and MCP Risks
What is AI Agent security? Explore MCP, Tool Calling, Prompt Injection, privilege escalation, data leakage and secure architecture for autonomous AI agents.
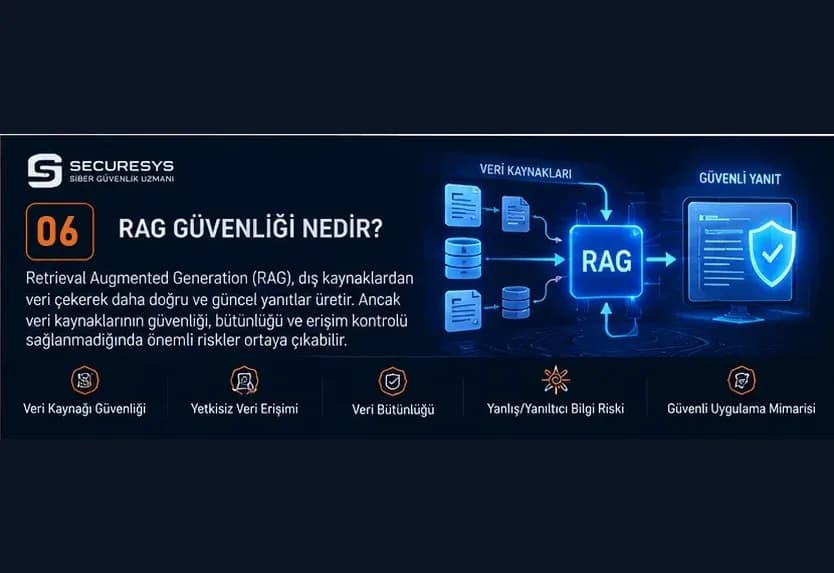
What Is RAG Security? Vector Database, Document Poisoning and Enterprise Data Leakage Risks
What is RAG security? Understand vector database, embedding, document poisoning, prompt injection and enterprise data leakage risks in RAG systems.
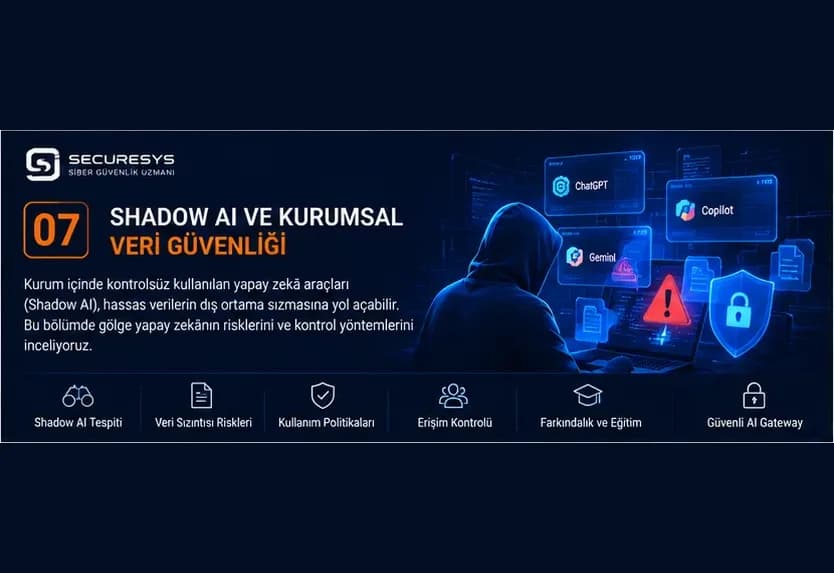
Shadow AI and Corporate Data Security: KVKK, GDPR and Protecting Sensitive Data in AI
What is Shadow AI? Uncontrolled employee AI use, corporate data leakage, KVKK, GDPR, AI DLP, data masking and AI Gateway methods to protect sensitive data.
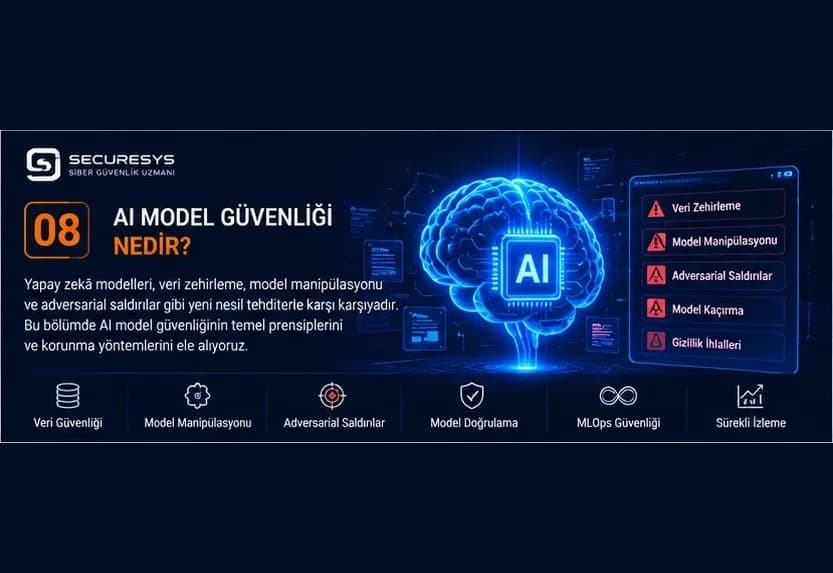
What Is AI Model Security? Protecting Against Data Poisoning, Model Theft and Adversarial Attacks
What is AI model security? Learn how Data Poisoning, Model Theft, Extraction, Inversion, Adversarial and Backdoor attacks work and how to defend against them.
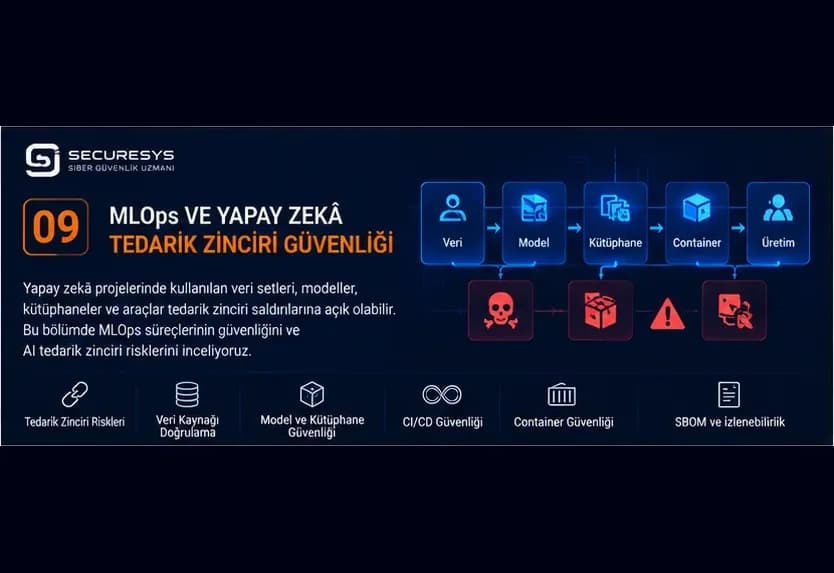
MLOps and AI Supply Chain Security: Model, Dataset and Pipeline Risks
What is MLOps security? Explore the AI supply chain, ML pipelines, model registries, dataset security, AI-BOM, model artifacts and Secure MLOps controls.
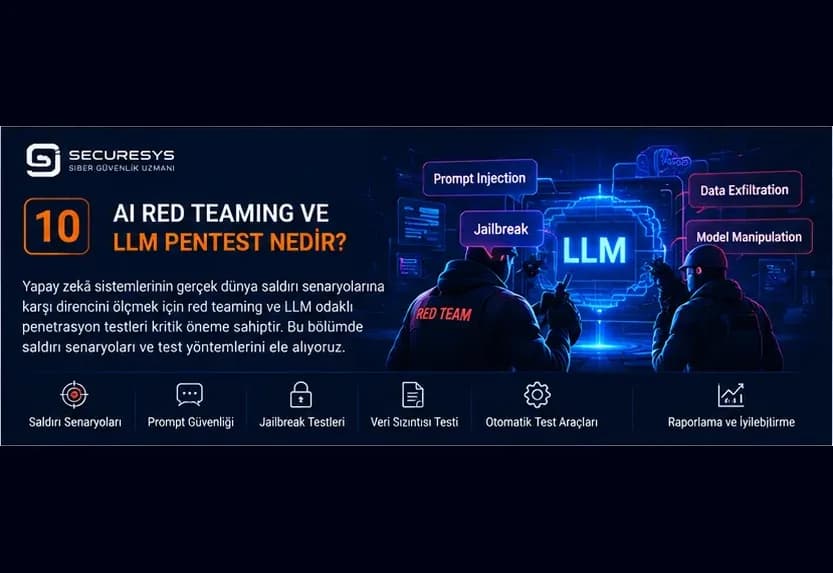
What Are AI Red Teaming and LLM Pentest? Security Testing for AI Applications
What are AI Red Teaming and LLM Pentest? Learn how prompt injection, jailbreak, RAG, AI agent, MCP, data leakage and model security tests protect AI systems.
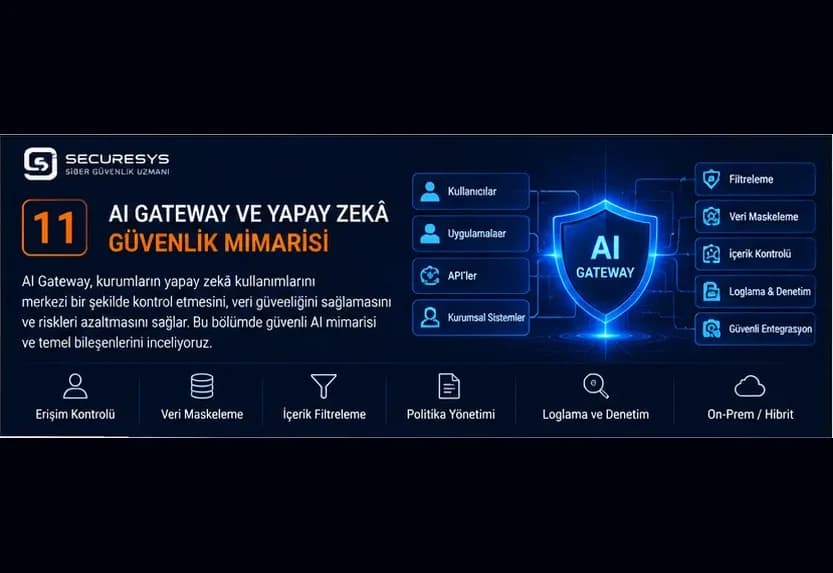
AI Gateway and AI Security Architecture: Prompt Firewall, DLP and Agent Control
What is an AI Gateway and how does it work? Explore Prompt Firewall, AI DLP, Shadow AI, Agent Security, Tool Calling, data masking and enterprise AI security.
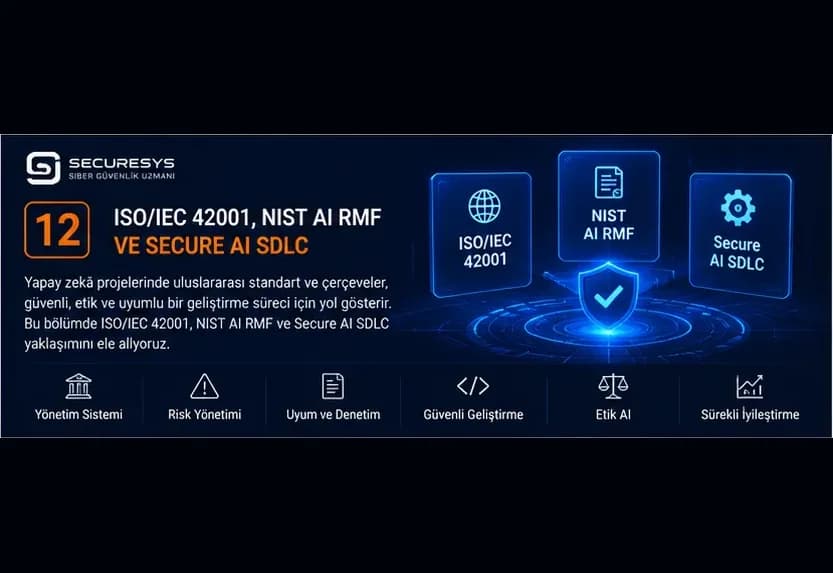
Enterprise AI Security Programme: ISO/IEC 42001, NIST AI RMF and Secure AI SDLC
How do you build an enterprise AI security programme? Explore ISO/IEC 42001, NIST AI RMF, Secure AI SDLC, AI governance, risk management and AI red teaming.
Looking for professional support on these topics?
Our expert team will reach out for a security assessment tailored to your organization.