Cyber Security Compliance & Advisory Centre
Cyber hygiene, ISO/IEC 27001, KVKK and GDPR, IEC 62443, NIS2, DORA and cyber security maturity models — a 12-part guide series on compliance and advisory processes prepared by our expert team.
What Is Cyber Hygiene? Essential Cyber Security Controls and Implementation Guide for Organisations
What is cyber hygiene and why does it matter? A guide to MFA, patch management, asset inventory, backup and access control for organisations.
Enterprise Cyber Hygiene Checklist: 25 Critical Security Controls and Implementation Guide
Enterprise cyber hygiene checklist: a guide to implementing 25 critical controls, from MFA, patch management and EDR to backup and access security.
What Is ISO/IEC 27001? ISMS, 93 Controls and Certification Guide
What is ISO/IEC 27001? Learn the 2022 standard, its 93 controls, ISMS setup, risk analysis, SoA, TÜRKAK accreditation and the certification process.
How to Perform an ISO/IEC 27001 Risk Analysis: Risk Assessment, Risk Treatment and SoA Preparation Guide
How is an ISO 27001 risk analysis done? 5×5 risk matrix, risk register, risk treatment plan, residual risk, SoA examples and an ISMS audit guide.
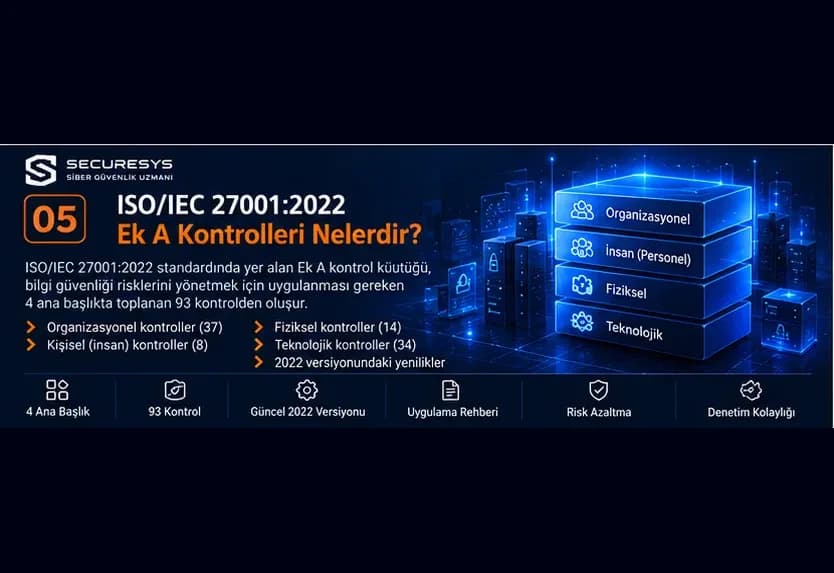
ISO/IEC 27001:2022 Annex A Controls: 93 Information Security Controls and Implementation Guide
Explore the 93 security controls in ISO 27001:2022 Annex A. Learn the organisational, people, physical and technological controls with implementation examples.
How to Conduct an ISO 27001 Internal Audit: Audit Plan, Nonconformity Management and Certification Readiness
How is an ISO 27001 internal audit done? Learn the audit plan, checklist, major and minor nonconformities, corrective actions and certification readiness.
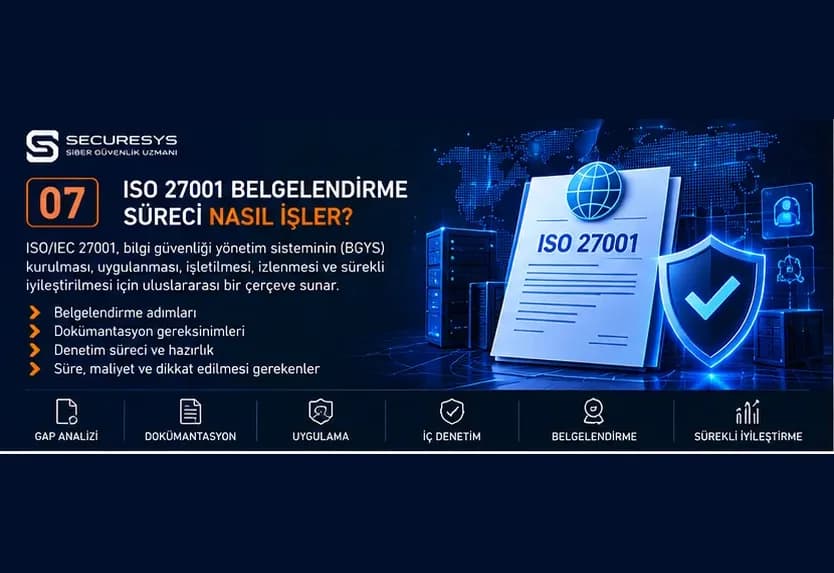
How Does the ISO 27001 Certification Process Work? A Guide to TÜRKAK, Stage 1, Stage 2 and Surveillance Audits
How do you get ISO 27001 certified? TÜRKAK accreditation, Stage 1 and Stage 2 audits, major and minor nonconformities, surveillance and certification costs.
How to Achieve KVKK and GDPR Compliance: A Guide to Personal Data Security, Technical and Administrative Measures
How to achieve KVKK and GDPR compliance: personal data inventory, technical and administrative measures, breach notification, transfers abroad and ISO 27001 controls.
What Is IEC 62443? Industrial Cyber Security, OT/ICS Security and IEC 62443-4-1 Consulting Guide
What is IEC 62443? Explore IEC 62443-4-1, 4-2, 3-3 and 2-1, OT/ICS security, industrial risk analysis, secure product development and certification consulting.
What Is the NIS2 Directive? EU Cybersecurity Obligations, Risk Management and Compliance Guide
What is the NIS2 Directive? Scope, 24 and 72-hour incident reporting, risk management, management accountability, fines and NIS2 compliance advisory.
What Is DORA? Digital Operational Resilience, Cyber Security and DORA Compliance Guide for Financial Entities
What is DORA? A guide to ICT risk management, incident reporting, TLPT, Red Team, third-party risk and DORA compliance consulting for financial entities.
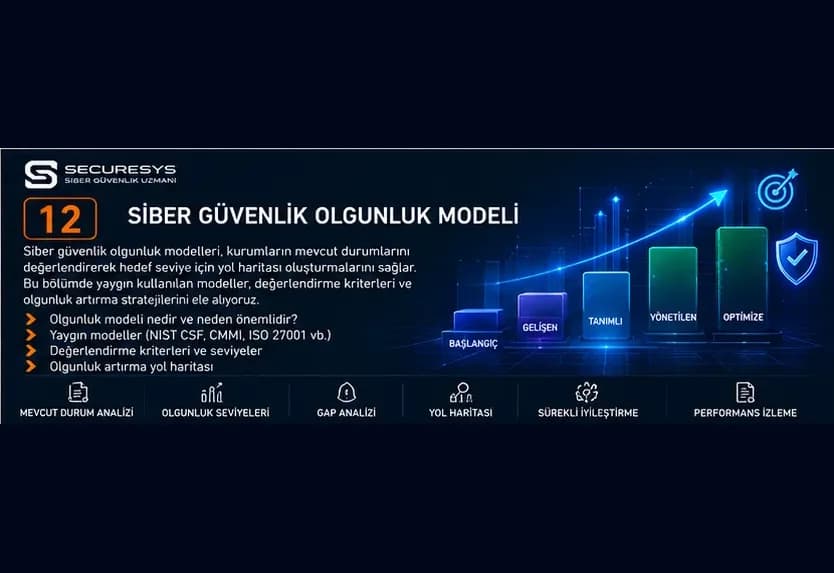
What Is a Cyber Security Maturity Model? Gap Analysis, Security Level Measurement and Enterprise Roadmap
What is a cyber security maturity model? NIST CSF 2.0, ISO 27001, IEC 62443, gap analysis, maturity levels and how to build an enterprise security roadmap.
Looking for professional support on these topics?
Our expert team will reach out for a security assessment tailored to your organization.